If your WordPress site still loads over http://, your visitors now hear about it before they see a single page. Starting with Chrome 154, Google’s browser tries HTTPS first and asks for permission before it opens any public site that can’t serve a secure connection. Firefox already shows a crossed-out padlock on plain HTTP pages, card payment rules require encryption at checkout, and Google has treated HTTPS as a ranking signal since 2014.
The good news: on most hosts, moving WordPress from HTTP to HTTPS is a one-afternoon job, and if you do it in the right order you won’t lose rankings. WordPress even has a one-click switch built into Site Health. The catch is that the button only covers part of the work. The parts it skips (old URLs in the database, hardcoded theme assets, redirects and Search Console) are exactly where migrations break.
This guide walks through the full migration in the order you should run it on a live site, with copy-ready code for Apache, Nginx and WP-CLI, notes for multisite networks, and fixes for the problems that show up afterwards, like redirect loops and a stubborn “Not secure” label.
Table of contents
- Quick Answer: How to Move WordPress From HTTP to HTTPS
- Which HTTPS Setup Fits Your Site?
- What HTTPS, SSL and TLS Actually Mean
- Why Moving WordPress to HTTPS Matters Now
- How to Move WordPress From HTTP to HTTPS Step by Step
- Step 1: Back Up Your Site and Rehearse on Staging
- Step 2: Install an SSL Certificate
- Step 3: Switch WordPress to HTTPS
- Step 4: Replace Old HTTP URLs in the Database
- Step 5: Fix Mixed Content in Your Theme, Plugins and Builder
- Step 6: Redirect HTTP to HTTPS With a 301
- Step 7: Test Everything Before You Call It Done
- Step 8: Update Search Console, Sitemaps and Everything Outside WordPress
- Step 9 (Optional): Turn On HSTS After a Week of Stability
- Moving a WordPress Multisite Network to HTTPS
- Troubleshooting Common WordPress HTTPS Problems
- HTTPS Migration Checklist
- Questions About SSL Costs, IP Addresses, Rankings and Redirects
- Make HTTPS the Default and Keep It That Way
Quick Answer: How to Move WordPress From HTTP to HTTPS
Here is how to move WordPress from HTTP to HTTPS without losing SEO, in eight steps. Each one is explained in detail below.
- Back up the site and, if you can, rehearse the move on a staging copy.
- Install an SSL certificate. A free Let’s Encrypt certificate from your host works for most sites.
- Switch WordPress to HTTPS in Tools > Site Health or Settings > General.
- Replace old http:// URLs in the database with a serialization-safe search and replace.
- Fix mixed content in your theme, plugins, widgets and page builder settings.
- Force HTTPS with a single 301 redirect at the server.
- Test the certificate, the redirects and every page template.
- Update your sitemap, Google Search Console, Bing Webmaster Tools, analytics, CDN and external profiles.
Once everything has been stable for about a week, consider turning on HSTS (step 9).
Before you start: plan on 30 to 90 minutes for a typical site, and longer for a large store or a multisite network. You’ll need administrator access to WordPress, access to your hosting panel or SFTP, and a fresh backup.
Which HTTPS Setup Fits Your Site?
The steps are the same for everyone, but the best tool for each step depends on where your site runs. Find your row, then follow the step-by-step section below.
| Your setup | Certificate | Switch WordPress | Redirect | Clean up old URLs |
|---|---|---|---|---|
| Shared or managed hosting | Free Let’s Encrypt or AutoSSL from your control panel | Site Health button | Your host’s Force HTTPS toggle | Better Search Replace |
| VPS or dedicated server | Certbot with automatic renewal | Settings > General or wp-config.php | .htaccess or Nginx rule | WP-CLI |
| Behind Cloudflare or another proxy | Certificate on your server plus Full (strict) mode | Settings > General plus the proxy fix in wp-config.php | One layer only: Cloudflare or your server | WP-CLI or Better Search Replace |
| Multisite network | One certificate, a wildcard, or one per mapped domain | Network Admin, site by site | Server rule | WP-CLI, once per site address |
What HTTPS, SSL and TLS Actually Mean
HTTPS is the regular web protocol (HTTP) running inside an encrypted connection. When a browser opens an HTTPS page, your server presents a certificate proving it controls the domain, and both sides agree on encryption keys. From then on, everything that travels between them, from login passwords and contact form entries to cookies and checkout details, can’t be read or altered by anyone in the middle, whether that’s someone on the same café Wi-Fi or a compromised router.
The “can’t be altered” part matters as much as the encryption. Without HTTPS, anyone controlling the network between you and a visitor can inject ads, tracking scripts or malware into your pages, and neither you nor your visitor will know it happened. If you want more background before getting practical, our primer explains what HTTPS is and why every site should use it.
A quick note on names. SSL (Secure Sockets Layer) is the original protocol, and it was retired years ago in favor of TLS (Transport Layer Security). A properly configured WordPress site today runs TLS 1.2 or TLS 1.3. Hosts, certificate sellers and plugins still say “SSL certificate”, and so does this guide, but they all mean the same thing.
How do you know it’s working? The address starts with https:// and the browser shows no warning. Don’t go looking for a green padlock: Chrome replaced the padlock with a neutral settings icon in 2023, so the absence of a “Not secure” label is now the real signal.
Why Moving WordPress to HTTPS Matters Now
Browsers Now Warn Visitors Before They Arrive
For years, an HTTP site only got a small “Not secure” label in the address bar. That changed with Chrome 154. As Google explained when it announced HTTPS by default for Chrome, the browser now turns on the “Always Use Secure Connections” setting for everyone. It attempts every public site over HTTPS first, and when a site can’t answer securely, it shows a full-page warning and asks the visitor to confirm before continuing. That’s a speed bump in front of your homepage, and every first-time visitor has to decide whether to trust you before seeing a single page.
Google rolled the setting out in stages, starting with Enhanced Safe Browsing users in Chrome 147, because only a small share of browsing still happens over plain HTTP. That’s the real message for site owners: an HTTP-only site is now the exception, and browsers treat it that way.
Logins, Forms and Checkouts Need Encryption
Every WordPress site has at least one form that sends sensitive data: the login page. Add contact forms, newsletter signups, membership areas or a WooCommerce checkout, and you’re collecting names, emails, addresses and passwords. Over plain HTTP, all of it crosses the network as readable text, and on public Wi-Fi that’s an open invitation to account takeovers.
If you sell online, HTTPS isn’t optional at all. Card industry rules (PCI DSS) require card data to be encrypted in transit, payment providers expect a secure checkout, and customers who see a browser warning on a payment page rarely come back to try again.
SEO, Trust and Cleaner Analytics
Google announced HTTPS as a ranking signal in 2014. It’s a lightweight signal, and switching won’t push a weak page to the top, but when Google finds the same page on both protocols it prefers to index the HTTPS version. More importantly, the browser warnings described above hurt clicks and engagement long before rankings move.
There’s also an analytics benefit people overlook. When someone clicks from an HTTPS site to an HTTP site, the browser strips the referrer, so that visit shows up as Direct in GA4 or any of the other website traffic analysis tools you rely on. If your site is still on HTTP, referral traffic from partners, directories and secure sites is quietly being misattributed.
Faster Protocols Require HTTPS
HTTPS used to be blamed for slowing sites down. Today it’s the opposite. Browsers only support HTTP/2 and HTTP/3 over encrypted connections, and those protocols load many files in parallel over a single connection. With TLS 1.3, setting up encryption adds just one round trip, and returning visitors can resume sessions even faster. Staying on HTTP locks your site out of the faster, modern way browsers load pages.
How to Move WordPress From HTTP to HTTPS Step by Step
The order below matters. Each step depends on the one before it, and doing them out of sequence (for example, forcing redirects before the certificate works) is the most common way to lock yourself out of your own dashboard.
Prefer to watch first? Our video tutorial covers the beginner version of this process:
Step 1: Back Up Your Site and Rehearse on Staging
Take a full backup of your files and database and store it somewhere other than your server. The database search and replace in step 4 is the riskiest part of this migration, and a backup is your only undo button. If you don’t have a backup routine yet, pick one of these WordPress backup plugins and keep it running after the migration too. It’s the cheapest insurance a WordPress site can have.
If your host offers one-click staging, run the whole process on the staging copy first. While you’re there, write down a few things you’ll need later:
- The current WordPress Address and Site Address from Settings > General.
- Whether
wp-config.phpdefinesWP_HOMEorWP_SITEURL. If it does, those constants override the dashboard settings. - Whether your site sits behind Cloudflare, a load balancer or another proxy. This changes how redirects must be written (see the troubleshooting section).
- Which page builder, caching plugin and CDN you use, since each one stores URLs or cached copies of your pages.
Step 2: Install an SSL Certificate
You need a valid certificate before WordPress can switch to HTTPS. How you get a free SSL certificate depends on your hosting:
- Shared and managed hosting: Most hosts include free Let’s Encrypt or AutoSSL certificates. Look for an SSL/TLS section in cPanel, Plesk or your host’s dashboard, issue the certificate and make sure it covers both
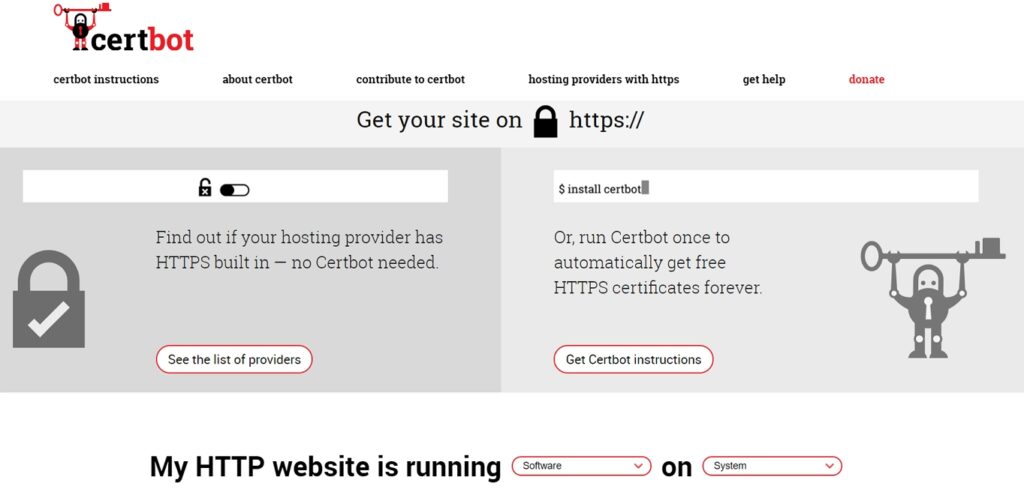
example.comandwww.example.com. - VPS or dedicated server: Use Certbot from the Electronic Frontier Foundation. You choose your web server and operating system, and it installs a Let’s Encrypt certificate and sets up automatic renewal.
- Cloudflare: Cloudflare can serve a certificate at its edge, but you still want a certificate on your own server. Set the SSL/TLS encryption mode to Full (strict). Flexible mode leaves the connection to your server unencrypted and is the classic cause of WordPress redirect loops.
- Hosts without free certificates: If your host charges extra for basic SSL or doesn’t support Let’s Encrypt at all, take it as a strong sign it’s time to move hosts.
For almost every WordPress site, a free domain-validated (DV) certificate is all you need. Paid OV and EV certificates verify your organization, which some compliance programs ask for, but browsers display them the same way and Google doesn’t rank them higher. You also don’t need a dedicated IP address: modern browsers support Server Name Indication (SNI), which lets many HTTPS sites share one IP. If you’re weighing a paid option, read these common myths about SSL certificates first.
Renewal matters more than it used to. According to Let’s Encrypt’s published timeline, its certificates last 90 days by default, dropping to 64 days on February 10, 2027 and to 45 days on February 16, 2028. Industry rules will cap every public certificate at 47 days by 2029, paid ones included. Hosts handle renewal for you, but if you manage your own server, confirm renewal runs on its own and doesn’t depend on a fixed 60-day schedule.
Before moving on, open https://yourdomain.com in a browser. The page may look broken or show warnings about insecure content, and that’s fine at this stage. What matters is that the browser accepts the certificate without a full-page error.
Step 3: Switch WordPress to HTTPS
With a working certificate in place, tell WordPress to use its HTTPS address. There are three ways to do it.
Option A: the one-click button in Site Health. WordPress 5.7 added HTTPS detection and one-click migration to Site Health. Go to Tools > Site Health. If WordPress detects that your server supports HTTPS but the site isn’t using it, the Status tab shows “Your website does not use HTTPS” with an Update your site to use HTTPS button. Click it, and WordPress updates both site addresses and logs you out.
There are two limits to know. The button only appears when the WordPress Address and Site Address are identical and aren’t set in wp-config.php. And WordPress fixes old http:// links on the fly as pages render, but it doesn’t rewrite them in the database. That’s why step 4 still matters.
Option B: Settings > General. Change both the WordPress Address (URL) and the Site Address (URL) from http:// to https://, then save. You’ll be asked to log in again.

Option C: wp-config.php. If those two fields are greyed out, the addresses are defined in wp-config.php. Edit them there:
define( 'WP_HOME', 'https://example.com' );
define( 'WP_SITEURL', 'https://example.com' );
Optionally, add this line to wp-config.php, above the comment that starts with “That’s all, stop editing!”, to keep logins and admin sessions encrypted even if a setting gets reverted later:
define( 'FORCE_SSL_ADMIN', true );Prefer a plugin? Really Simple Security (formerly Really Simple SSL) detects your certificate, switches the URLs, adds redirects and fixes common mixed content in a few clicks. It’s a reasonable choice for beginners. Just know that if the plugin is the thing doing your redirects, deactivating it later removes them, so server-level redirects (step 6) are the sturdier long-term setup.
Step 4: Replace Old HTTP URLs in the Database
Every image you’ve inserted, every internal link and every button in your page builder was saved with the full http:// address. Changing the site address doesn’t touch any of that, so you need a search and replace across the database.
If you have SSH access, WP-CLI is the safest tool because it handles serialized data correctly. Run a dry run first to see what would change, then run it for real:
wp search-replace 'http://example.com' 'https://example.com' --all-tables --skip-columns=guid --dry-run
wp search-replace 'http://example.com' 'https://example.com' --all-tables --skip-columns=guid
If your site ever used the www version, run it for http://www.example.com as well. The --skip-columns=guid flag leaves post GUIDs alone, since they’re permanent identifiers that feed readers rely on, not links visitors click.
No command line? Install Better Search Replace from the plugin directory. Enter the old and new URLs, select all tables, leave the GUID option unchecked and run it as a dry run before the real pass.
Whatever you do, don’t run a raw SQL REPLACE query on the database. WordPress stores widget settings, theme options and builder layouts as serialized data that includes character counts, and a plain find-and-replace corrupts them. That’s how people end up with empty sidebars and lost theme settings. When you’re done, clear every cache: plugin, server and CDN.
Step 5: Fix Mixed Content in Your Theme, Plugins and Builder
Mixed content means an HTTPS page is still loading something over HTTP. Browsers block insecure scripts and frames outright and either upgrade or block insecure images, so you’ll see missing elements, broken layouts or a “Not secure” label even though your certificate is fine.
The database search and replace catches most of it. The WordPress mixed content that remains usually hides in places WordPress doesn’t store as post content:
- Logo, favicon and background image URLs in theme options or the Customizer
- Additional CSS and theme stylesheets with
url(http://...)backgrounds - Scripts and styles hardcoded in
functions.php, header templates or a child theme - Custom links in menus and in text or HTML widgets
- Global settings in page builders and slider plugins
- Embedded iframes, web fonts and old third-party scripts such as chat widgets, legacy analytics and ad code
To find them, open a page, press F12 and check the Console tab. Chrome lists every insecure request with a “Mixed Content” warning and the exact URL. Repeat this on each template type, not just the homepage.
Fix each one by changing it to https:// or to a root-relative path such as /wp-content/uploads/logo.png. Older tutorials recommended protocol-relative URLs that start with //. Skip that advice: once your site is fully on HTTPS, there’s no reason to request any asset over HTTP, and a plain https:// link is clearer. If a third-party resource has no HTTPS version at all, replace it or remove it.
As a temporary safety net while you clean up, you can send the Content-Security-Policy: upgrade-insecure-requests header, which tells browsers to request every asset over HTTPS. Treat it as a stopgap, not a fix.
Step 6: Redirect HTTP to HTTPS With a 301
Now make HTTPS the only version anyone can reach. A permanent (301) redirect is what actually forces HTTPS across your WordPress site: it sends visitors, old bookmarks, backlinks and search engine crawlers to the secure URL and tells Google the move is permanent.
Apache or LiteSpeed: Edit the .htaccess file in your WordPress root folder. It’s hidden by default, so enable “show hidden files” in your FTP client or file manager. If the file doesn’t exist, create a plain text file with that name. Add these lines above the # BEGIN WordPress block so WordPress never overwrites them:
<IfModule mod_rewrite.c>
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
</IfModule>
Nginx: Add a server block that listens on port 80 and redirects everything, then reload Nginx:
server {
    listen 80;
    server_name example.com www.example.com;
    return 301 https://example.com$request_uri;
}
Hosting panels and Cloudflare: Many hosts have a “Force HTTPS” toggle, and Cloudflare has “Always Use HTTPS”. Either works, but pick one place to handle the redirect. Stacking the same rule in a plugin, in .htaccess, in your host’s panel and in Cloudflare is how redirect loops happen.
Aim for as few hops as possible. Someone visiting http://www.example.com/page/ should land on https://example.com/page/ (or your preferred www version) in one redirect, not three. This command shows every hop for a URL:
curl -sIL http://www.example.com/sample-page/ | grep -i -E "^(HTTP|location)"Finally, make sure no page answers on both protocols. If the http:// and https:// versions of a page both load with a 200 status, Google sees duplicate content and has to guess which one to keep.
Step 7: Test Everything Before You Call It Done
Don’t stop at the homepage. Work through this short test pass:
- Certificate quality: Run your domain through the Qualys SSL Labs Server Test. An A grade confirms the certificate chain, supported TLS versions and server settings are correct.
- Redirects: Request a few old http:// URLs (the homepage, a post, an image and a category page) and confirm each returns a 301 to the matching HTTPS URL, not to the homepage.
- Templates: Open each page type in a private window with DevTools open: home, single post, page, archive, search, 404, login, contact form and, for stores, cart, checkout and account pages.
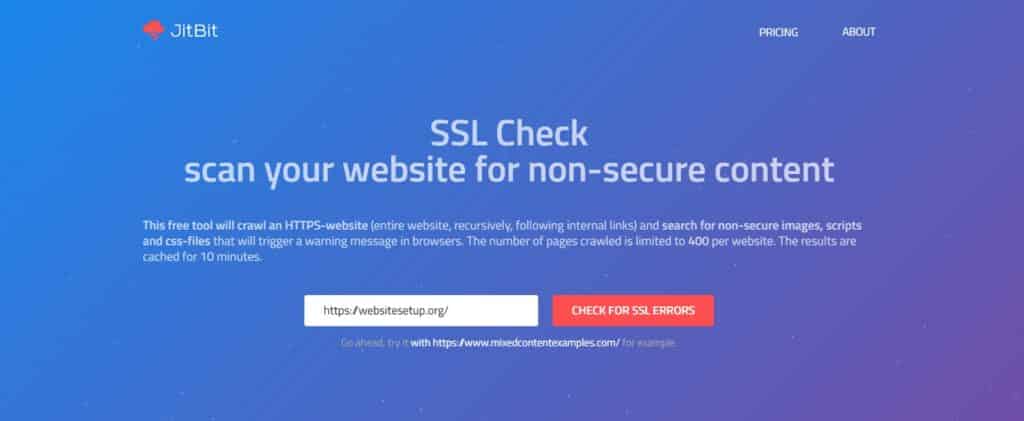
- Internal links: Crawl the site with an SEO crawler such as Screaming Frog to catch leftover http:// links, redirect chains and canonical tags that still point to HTTP.
- The visitor’s view: In Chrome, open
chrome://settings/security, confirm “Always use secure connections” is on, then browse your site the way a new visitor would.
Then submit a test form, place a test order if you run a store, and check that notification emails and webhooks still arrive.
Step 8: Update Search Console, Sitemaps and Everything Outside WordPress
Your site is secure now, but plenty of places outside WordPress still point to the old address.
XML sitemap and robots.txt. Yoast SEO, Rank Math and the WordPress core sitemap build URLs from your site address, so they should switch to HTTPS automatically. Open the sitemap and confirm every URL starts with https://. If some don’t, clear your cache and resave Settings > Permalinks. If you’re choosing or replacing a sitemap generator, compare these WordPress sitemap plugins. Also check that the Sitemap line in robots.txt uses the HTTPS address.
Google Search Console. If you verified your site as a Domain property, it already covers both protocols, so just resubmit the HTTPS sitemap. If you use URL-prefix properties, add and verify https://example.com as a new property and submit the sitemap there. If you ever uploaded a disavow file, upload it to the new property too. Don’t use the Change of Address tool: Google says it isn’t meant for protocol changes, and Google’s guide to site moves with URL changes explains what it does expect, mainly clean 301 redirects, HTTPS canonical tags and an updated sitemap.
Expect some crawling and ranking movement for a few weeks while Google processes the new URLs. Watch the Pages and Sitemaps reports: indexed HTTPS URLs should climb as the HTTP ones fall away.
Bing Webmaster Tools. Bing’s index also feeds Microsoft Copilot, so don’t skip it. Add the HTTPS site, or import your properties from Google Search Console, and submit the same sitemap.
Analytics and ads. GA4 keeps tracking because it records whatever URL the page loads on, but update the website URL in Google Ads final URLs, Merchant Center, Google Business Profile and any other tool where your address is stored.
CDN. If you use a content delivery network, enable HTTPS there, make sure it fetches from your server over HTTPS and purge the full cache so no visitor gets an old HTTP copy.
Everything else. Update the link on your social profiles (an easy win if social media marketing brings you traffic), plus email signatures and templates, newsletter footers, directory listings and payment or form webhooks. If a few high-value sites link to you, ask them to update the URL. The redirect passes visitors along either way, but a direct link is cleaner.
Share counters are the one casualty to plan for. Social networks count shares per URL, so counters tied to the old http:// address may reset to zero. Some social sharing plugins can recover the old counts if that matters to you.
Step 9 (Optional): Turn On HSTS After a Week of Stability
HTTP Strict Transport Security (HSTS) tells browsers to always use HTTPS for your domain, even if someone types http:// or clicks an old link. It closes the small gap before the first redirect, when a visitor is still on an insecure connection.
Only enable it once everything has been stable for a while, because browsers remember the rule for the full max-age period. Test with a short value such as max-age=300 first, then raise it to one year. On Apache with mod_headers enabled, the final version in .htaccess looks like this:
<IfModule mod_headers.c>
Header always set Strict-Transport-Security "max-age=31536000; includeSubDomains"
</IfModule>
Leave out includeSubDomains if any subdomain still runs on HTTP, and don’t submit your domain to the HSTS preload list unless you’re sure every subdomain will stay on HTTPS permanently. Getting a domain removed from that list can take months. For deeper server tuning such as OCSP stapling, our server-level HTTPS migration checklist for Apache and Nginx covers the configuration side.
Moving a WordPress Multisite Network to HTTPS
A multisite network follows the same steps, with three differences:
- Certificates: A subdirectory network (example.com/shop/) needs only one certificate. A subdomain network (shop.example.com) needs a wildcard certificate for *.example.com, and Let’s Encrypt only issues wildcards through DNS validation, so your host or DNS provider has to support it. Every mapped custom domain needs its own certificate.
- Site addresses: Don’t rely on the Site Health button here. Each site keeps its own Siteurl and Home values, which you can check and edit under Network Admin > Sites > Edit, on the Settings tab.
- Database URLs: A search for http://example.com won’t match http://shop.example.com, so run the search and replace from step 4 once for every site address. The
--all-tablesflag already covers every site’s tables, and this command lists the addresses you need:
wp site list --field=urlTroubleshooting Common WordPress HTTPS Problems
Most HTTPS migrations go smoothly. When one doesn’t, the cause is almost always on this list.
Too Many Redirects (ERR_TOO_MANY_REDIRECTS)
A “too many redirects” error means two rules are sending the browser in circles. The usual causes:
- Cloudflare set to Flexible SSL. Cloudflare talks to your server over HTTP, your server redirects to HTTPS, and Cloudflare requests HTTP again. Switch the encryption mode to Full (strict).
- A proxy or load balancer that handles HTTPS for you. WordPress sees every request as HTTP and keeps redirecting. Fix it with the
wp-config.phpsnippet below. - Duplicate redirect rules in a plugin, in .htaccess, in your host’s panel and in your CDN. Keep one and remove the rest.
- Mismatched addresses, such as https:// in Settings > General but an http:// value in
WP_HOME.
For sites behind a proxy, add this to wp-config.php above the “That’s all, stop editing!” comment:
if ( isset( $_SERVER['HTTP_X_FORWARDED_PROTO'] ) && 'https' === $_SERVER['HTTP_X_FORWARDED_PROTO'] ) {
    $_SERVER['HTTPS'] = 'on';
}
If you redirect in .htaccess behind a proxy, also replace the RewriteCond %{HTTPS} off line with RewriteCond %{HTTP:X-Forwarded-Proto} !https. Then test in a private window, because browsers cache 301 redirects aggressively.
Your Site Still Shows Not Secure After Installing SSL
If there’s no full-page error but the address bar still warns, it’s mixed content. Go back to step 5 and check the Console on the exact page showing the warning. If the browser shows a full-page error such as NET::ERR_CERT_COMMON_NAME_INVALID instead, the certificate doesn’t cover the hostname you’re visiting, most often the www version. Reissue it with both names included.
Locked Out of wp-admin After Changing the URL
If you changed the site address before the certificate worked, you may not be able to log in. Connect over FTP or your host’s file manager and add these lines to wp-config.php to force the old address temporarily:
define( 'WP_HOME', 'http://example.com' );
define( 'WP_SITEURL', 'http://example.com' );
If you already added an HTTPS redirect, comment it out in .htaccess too. Log in, fix the certificate, switch back to https:// as described in step 3 and remove the temporary lines. If a plugin caused the lockout, rename its folder inside wp-content/plugins to deactivate it.
The Certificate Expired or Didn’t Renew
Let’s Encrypt renewals are automatic, but they can fail silently: the domain’s DNS moved, a firewall or CDN rule blocks the validation request, or a scheduled job stopped running. Check your hosting panel’s SSL section, or run certbot renew --dry-run on a VPS. With certificate lifetimes shrinking over the next few years, an uptime monitor that alerts you before a certificate expires is cheap insurance.
WordPress Can’t Connect to WordPress.org After the Switch
If plugin and theme updates fail with a message saying WordPress could not establish a secure connection, the problem is on the server side (usually cURL, OpenSSL or a firewall), not your certificate. Our guide to fixing the unable to establish secure connection error walks through each cause.
Redirects or Scripts You Didn’t Add
If your pages redirect to unfamiliar domains, or the Console shows insecure scripts loading from sites you never added, don’t treat it as a normal migration glitch. Injected redirects and scripts are classic signs of a compromised site. Pause the migration, keep a copy of the infected files for analysis and follow a hacked WordPress site response plan before going any further.
HTTPS Migration Checklist
Use this as a final pass, or keep it open and tick items off as you go.
| Task | Where to do it | How to confirm it worked |
|---|---|---|
| Full backup taken | Backup plugin or host | The backup file downloads and opens |
| Certificate covers both domain versions | Hosting panel, Certbot or Cloudflare | No certificate errors on https:// with and without www |
| Site addresses switched to HTTPS | Site Health, Settings > General or wp-config.php | Both address fields start with https:// |
| Database URLs replaced | WP-CLI or Better Search Replace | A new dry run finds no http:// matches for your domain |
| Mixed content fixed | Theme options, widgets, builder, CSS | No Mixed Content warnings in the browser console |
| 301 redirect active | .htaccess, Nginx, host panel or CDN (one only) | Old URLs return a 301 to the matching HTTPS URL |
| Canonicals and sitemap on HTTPS | SEO plugin | Page source and sitemap show only https:// URLs |
| Search engines updated | Google Search Console and Bing Webmaster Tools | Sitemap submitted and HTTPS pages being indexed |
| CDN, ads and profiles updated | CDN dashboard, Google Ads, social profiles | Every stored URL uses https:// |
| Renewal confirmed | Host panel or certbot renew –dry-run | The renewal test completes without errors |
Questions About SSL Costs, IP Addresses, Rankings and Redirects
Usually, yes. Let’s Encrypt certificates cost nothing, and most hosts issue and renew them automatically from the control panel. Paid OV or EV certificates add business verification that some compliance programs require, but browsers display them the same way as free certificates and Google does not rank them higher.
No. Server Name Indication (SNI), which every modern browser supports, lets many HTTPS sites share one IP address, so shared hosting plans can give every site on a server its own certificate. A dedicated IP is only worth paying for if a specific integration or a very old client requires it.
Not if the redirects are set up correctly. Google treats an HTTP to HTTPS switch as a site move with URL changes and generally processes it well. Expect some ranking and crawl fluctuation for a few weeks. Lasting drops almost always trace back to redirect chains, canonical tags or sitemaps still pointing to HTTP, or pages that load on both protocols.
No. Since WordPress 5.7, the Site Health screen under Tools can switch your site addresses with one click, and a server-level 301 redirect plus a database search and replace cover the rest. Really Simple Security (formerly Really Simple SSL) is convenient for beginners, but if it handles your redirects, deactivating it later removes them.
No. Google says the Change of Address tool is not meant for HTTP to HTTPS moves and that it works out the protocol change on its own. Use permanent 301 redirects, HTTPS canonical tags and an HTTPS sitemap, then monitor the Pages and Sitemaps reports in Search Console.
Either the page still loads something over HTTP (mixed content) or the certificate does not cover the address you visited, often the www version. Open the browser console with F12 on the affected page to see insecure requests, and reissue the certificate with both the www and non-www names if the browser shows a certificate error.
Permanently. Old backlinks, bookmarks, emails and social posts will point to http:// addresses for years, and the redirect costs nothing to keep. Removing it would send that traffic to an insecure page or an error.
Make HTTPS the Default and Keep It That Way
Moving WordPress from HTTP to HTTPS isn’t hard, but it rewards doing things in order: certificate first, then the WordPress settings, then the database, then mixed content, then one clean 301 redirect, and finally the Search Console and analytics cleanup that keeps your rankings intact.
Once the switch is live, two habits keep it healthy. Check that your certificate renews on its own, because lifetimes keep getting shorter, and whenever you add a new plugin, embed or script, make sure it loads over HTTPS. Do that, and “Not secure” becomes a warning your visitors never see on your site.
If you’d rather not edit server files yourself, Visualmodo’s Advanced Support team can install your SSL certificate or handle the full WordPress migration as a one-off service.